
Secure Password Storage with Password Hashing
InPassword hashing converts a password into a one-way value suitable for storage. PHP automatically includes a salt, so the previoussame tutorial,password can produce different valid hashes.
Use fictional test passwords
wereonly.storedNeveras plain text in the database. In this tutorial, you will updateenter yourprojectschool,toemail,storebankingpasswordsorsecurelyreusedusingpersonalPHP password hashing.password.
Why Hash Passwords?
When passwords are stored as plain text, anyone with access to the database can read them.
Example:
A hashed password looks like this:
$2y$10$F8xJYQjN8s0T8f9mK6n7Iu8j9L2mWm9J4hJj7Qz0vB5lK3sHn8QyW
The original password cannot easily be recovered from the hash.
CreateGenerate a Password Hashhash
Create a new PHP file called:
hash_password.php
Add the following code:
<?php
$passwordtestPassword = "password123"fictional-test-password";
$hashedPasswordhash = password_hash($password,testPassword, PASSWORD_DEFAULT);

echo htmlspecialchars($hashedPassword;hash, ?>ENT_QUOTES, "UTF-8");
SaveStore the filecomplete hash in your web server folder and run it in your browser.
Example:
http://localhost/hash_password.php
You should see a long string similar to:
$2y$10$F8xJYQjN8s0T8f9mK6n7Iu8j9L2mWm9J4hJj7Qz0vB5lK3sHn8QyW
Copy the Hash
Select and copy the generated hash.
You will use this value instead of the plain text password.
Update the Admin Account
Open phpMyAdmin.
Select the usersVARCHAR(255)table.
Locatefield. theDo adminaccountshorten and click Edit.
Replace:
password123
with your generated password hash.
Click Go to save the changes.
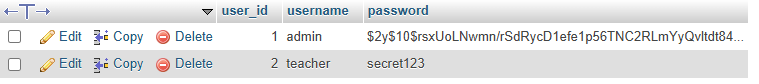
Verify the Password Was Updated
Run:
SELECT * FROM users;
The password column should now contain a long hash instead of a readable password.
Example:
Verify a Passwordsubmitted password
Create a new file called:
verify_password.php
Add the following code:
<?php
$passwordsubmittedPassword = "password123"fictional-test-password";
$hashstoredHash = '$2y$10$F8xJYQjN8s0T8f9mK6n7Iu8j9L2mWm9J4hJj7Qz0vB5lK3sHn8QyW'REPLACE_WITH_A_COMPLETE_HASH';

if (password_verify($password,submittedPassword, $hash)storedHash)) {
    echo "Password is correct"accepted.";
} else {
    echo "Password isnot incorrect"accepted.";
}

?>
ReplaceLogin code should retrieve the examplestored hash withby yourusername ownand generatedpass hash.
Opento password_verify(). Never hash the filesubmitted inpassword youragain browser.and compare strings; salts make that unreliable.
Example:
Rehash when needed
http:if (password_needs_rehash($storedHash, PASSWORD_DEFAULT)) {
    $newHash = password_hash($submittedPassword, PASSWORD_DEFAULT);
    //localhost/verify_password.php Update the stored hash using a prepared statement.
}
YouThis shouldallows see:PHP’s current default algorithm to improve over time.
PasswordSafe is correct
Test an Incorrect Passwordpractice
Change:
$password = "password123";
to:
$password = "wrongpassword";
Refresh the page.
You should now see:
Password is incorrect
Common Mistake
md5()passwords.not place passwords or
sha1()connection in screenshots.
Do not email or log submitted passwords. Use HTTPS on hosted systems. Use prepared statements forModernupdates.
generic.
Check
password_hash()
password_verify()
These functions automatically use secure hashing algorithms and are updated as PHP improves.
Complete Example
Generate a Hash
<?php

$password = "password123";

$hashedPassword = password_hash($password, PASSWORD_DEFAULT);

echo $hashedPassword;

?>
Verify a Password
<?php

$password = "password123";

$hash = '$2y$10$YOUR_HASH_HERE';

if (password_verify($password, $hash)) {
echo "Password is correct";used }during elseregistration.password_verify() is VARCHAR(255).
You